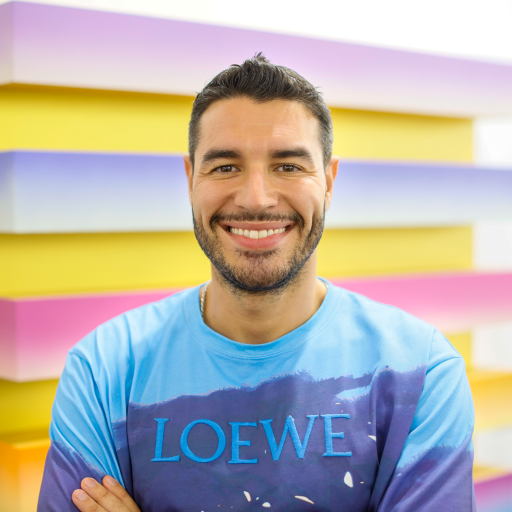
Hello! My name is Matt Suiche. I work on AI Security at Tolmo, and I also experiment with side projects in AI Safety (Weightless, etc.) and Emulation & Operating System Research (WASM PSX, WASM NanoKrnl, etc.). I recently discussed cyberwar in the age of AI, Iran’s cyber capabilities, and how AI is reshaping hacking on Bloomberg’s Odd Lots and the National Security Lab podcast.
Previously, I founded OnDB Inc., a data infrastructure startup for the agentic economy, and co-founded CloudVolumes (acquired by VMware in 2014) and Comae Technologies (acquired by Magnet Forensics in 2022), where I later served as Head of Detection Engineering. I also founded the cybersecurity community project OPCDE.
My path into technology started in reverse engineering as a teenager, and has since spanned memory forensics, operating systems, virtualization, blockchain, and now AI infrastructure.
The 14 detectors and ~62 rules aren't the interesting part. The interesting part is that the same loop that built them is the loop that repairs them when production surfaces a false positive — usually within an hour, costing under a dollar. …
Pulled the full OSV mirror for npm and PyPI — 230,000+ advisories. The malicious-tagged subset clusters into five recurring patterns. None of them are clever. All of them keep working. A note on why two decades of EDR/XDR investment is …
A scoped audit of the leaked Windows 2000 source tree turned up 45 findings mapped against 24 public CVEs spanning 1999 to 2025 — including four bugs that took Microsoft between 6 and 25 years to patch, plus the WMI EoPs R00tkitSMM found by …