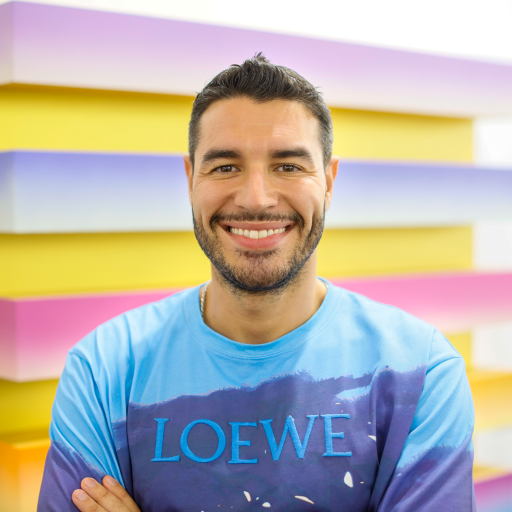
Hello! My name is Matt Suiche. I work on AI Security at Tolmo, and I also experiment with side projects in AI Safety (Weightless, etc.) and Emulation & Operating System Research (WASM PSX, WASM NanoKrnl, etc.). I recently discussed cyberwar in the age of AI, Iran’s cyber capabilities, and how AI is reshaping hacking on Bloomberg’s Odd Lots and the National Security Lab podcast.
Previously, I founded OnDB Inc., a data infrastructure startup for the agentic economy, and co-founded CloudVolumes (acquired by VMware in 2014) and Comae Technologies (acquired by Magnet Forensics in 2022), where I later served as Head of Detection Engineering. I also founded the cybersecurity community project OPCDE.
My path into technology started in reverse engineering as a teenager, and has since spanned memory forensics, operating systems, virtualization, blockchain, and now AI infrastructure.
Offline domain join is a new process that joins computers running Windows® 7 or Windows Server 2008 R2 to a domain in Active Directory Domain Services (AD DS)—without any network connectivity. This process includes a new command-line tool, …
Here is a method I’m using in the next version of Win32DD (1.2), to retrieve MmPhysicalMemoryBlock regardless of the NT Version. The main problem with KDDEBUGGER_DATA64 structure is the version dependency. Then, we have to rebuild this …
Today, I wrote a tool called sym32guid which aims at retrieving all stored Program DataBase (*.PDB File) GUID (Globally Unique Identifier) from a physical memory dump. To do why? The first goal was to use use symbols as additional …